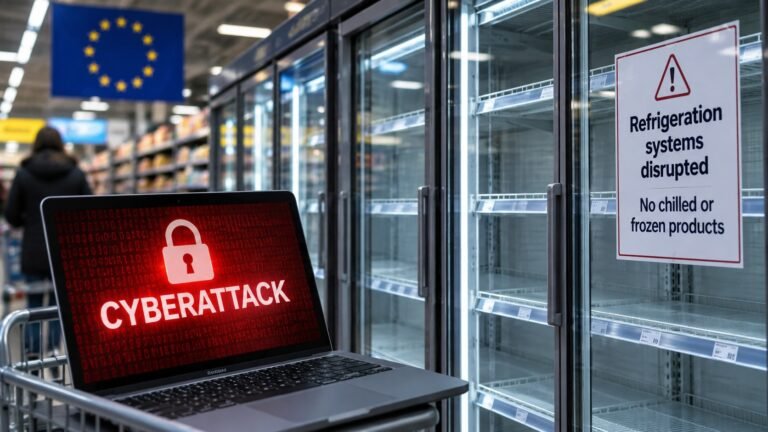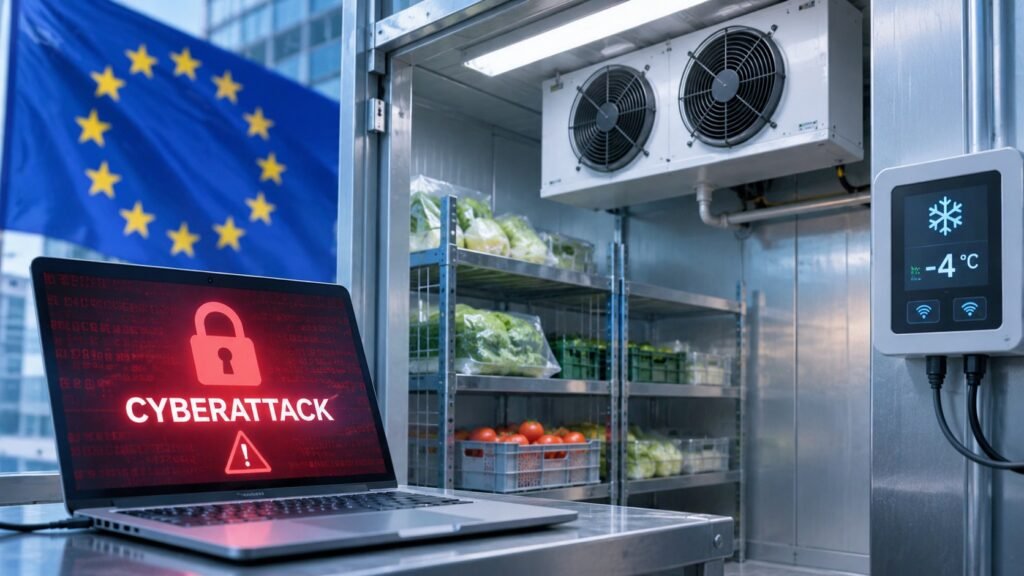
The European Commission and the European Union Agency for Cybersecurity (ENISA) have called on businesses to take immediate cybersecurity measures following attacks targeting commercial refrigeration systems across several EU member states. A joint statement issued on November 4, 2026, confirmed incidents affecting refrigeration systems and similar connected devices since October 11, followed by another wave of attacks on November 1–2.
The Commission and ENISA are coordinating with national authorities to monitor the incidents, exchange information and assess the situation. The response involves the Commission’s Directorate-General for Communications Networks, Content and Technology (DG CNECT), Europol’s European Cybercrime Centre (EC3), the EU Computer Security Incident Response Teams Network and the European Cyber Crisis Liaison Organisation Network (EU-CyCLONe).
Organisations operating potentially vulnerable refrigeration equipment have been advised to take immediate steps to reduce their exposure to cyber threats. Affected EU member states are investigating the incidents and providing guidance to businesses, while national cybersecurity response teams and EU coordination bodies continue exchanging information.
The incidents come amid the implementation of EU cybersecurity legislation. Under the Cyber Resilience Act, manufacturers of hardware and software products have been required since September 11, 2026, to report severe security incidents and actively exploited vulnerabilities through the EU’s Single Reporting Platform. Additional requirements taking effect on December 11, 2027, will oblige manufacturers of products with digital elements to integrate security into product design, provide cybersecurity support throughout the product lifecycle and address vulnerabilities without delay.
Organisations covered by the NIS2 Directive must implement appropriate cybersecurity risk management measures and report significant incidents to relevant national authorities. ENISA and other EU cybersecurity bodies will continue monitoring developments and coordinating information-sharing as investigations proceed.