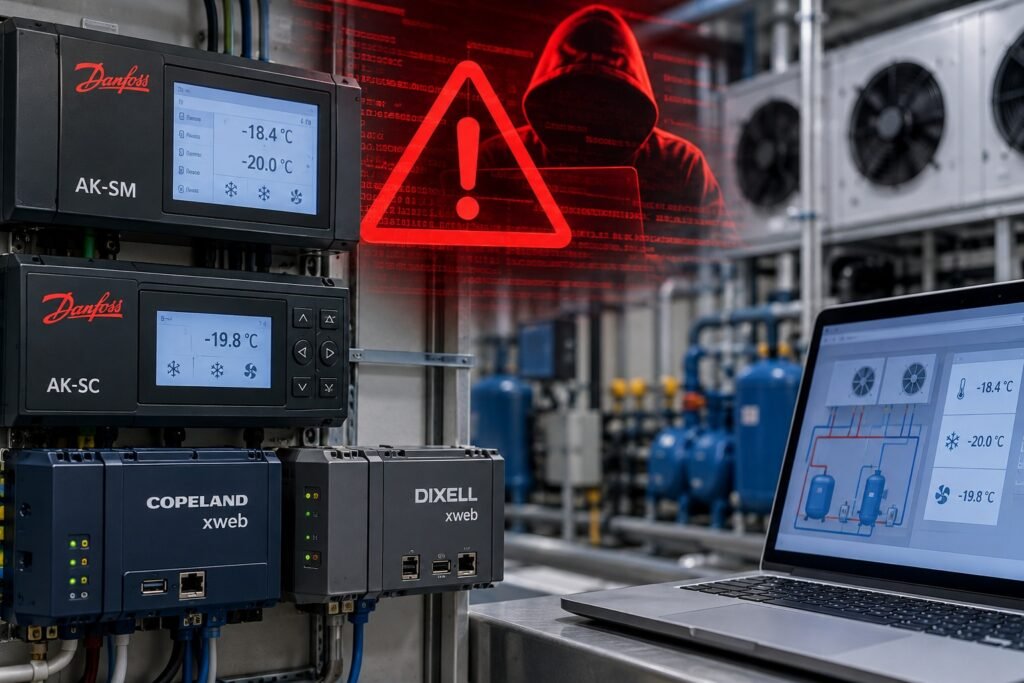
France’s national cybersecurity response team, CERT-FR, has reported numerous security compromises affecting remote controllers used in refrigeration installations. The alert, initially published on October 12, 2026, and updated on October 13, identifies Danfoss AK-SM and AK-SC series controllers, as well as Copeland xweb and Dixell xweb systems, among the affected equipment.
According to CERT-FR, exposing management interfaces directly to the Internet is contrary to cybersecurity best practices. The agency warns that attack campaigns targeting these controllers are probably still ongoing, with equipment that no longer receives security patches facing a particularly high risk of compromise.
For equipment that has not been compromised, CERT-FR recommends removing direct Internet exposure, including for other units accessible through public IP addresses, and checking the complete configuration, particularly defrost schedules. Before disconnecting Internet-based data transmission to refrigeration service providers, operators should verify their contractual insurance conditions.
Remote access should be restored only through a secure VPN or protected network. As an emergency measure, operators may restrict access to service providers’ IP addresses using firewall rules, although CERT-FR does not consider this a permanent solution. The agency also recommends following manufacturers’ security guidance, including firmware updates. For Danfoss controllers, specific measures include enabling Strict security mode and changing default passwords.
For compromised controllers, CERT-FR advises removing Internet exposure, performing a factory reset, reconfiguring the equipment and restoring access through a secure connection. However, the agency stresses that a factory reset alone is insufficient for end-of-life equipment without security patches. Although the reset removes persistence mechanisms from a compromised system, the underlying vulnerability remains, leaving the controller at risk of being compromised again.