Five US federal agencies have issued a joint warning about cyberattacks targeting industrial refrigeration and cold chain monitoring systems worldwide. The November 5, 2026, fact sheet from CISA, the FBI, HHS, USDA and the Department of Transportation urges operators to secure refrigeration controllers, restrict remote access and update vulnerable equipment.
The warning follows incidents affecting refrigeration systems in at least 11 European countries. In late October, hundreds of French supermarkets reported disruptions after attackers activated defrost cycles, raising temperatures to nearly 125°F (50°C) and damaging inventories. Similar incidents were subsequently reported in other European countries, including attacks targeting blood banks.
France’s CERT-FR reported compromises involving Danfoss AK-SM and AK-SC controllers and Copeland and Dixell XWEB systems. Investigators have not established responsibility for the incidents or determined whether they belong to a single campaign. Separately, the US Department of Defense is investigating suspected cyberattacks linked to refrigeration failures at at least six military commissaries in August.
According to the federal agencies, attackers may exploit authentication bypass vulnerabilities, arbitrary code injection and weak configurations to alter controller settings remotely. Potential consequences include continuous heating or defrost cycles, inventory losses, equipment hazards and loss of temperature monitoring visibility.
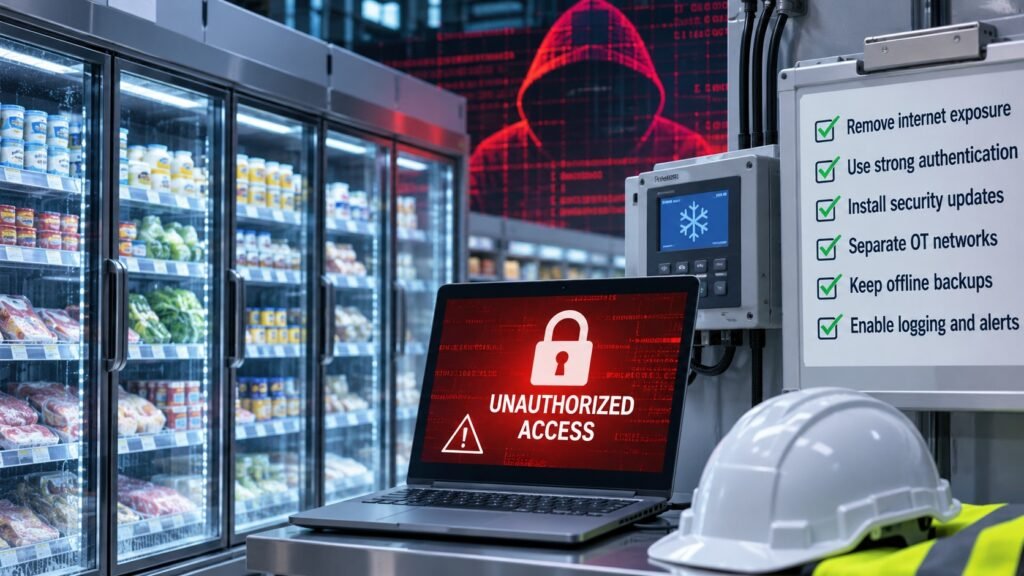
The agencies recommend removing controllers from direct internet exposure, separating operational technology networks from business networks, changing default passwords and implementing strong authentication. Additional measures include firmware updates, replacing unsupported devices, maintaining offline backups, reviewing activity logs and establishing safe temperature setpoint limits with alerts.
For refrigeration distributors and contractors, the incidents highlight the importance of communicating manufacturers’ security guidance and providing technical training for internet-connected systems. Contractors can help customers identify controllers, verify remote access settings and determine whether firmware updates are required. The federal guidance also recommends reporting suspicious activity to CISA or the FBI.