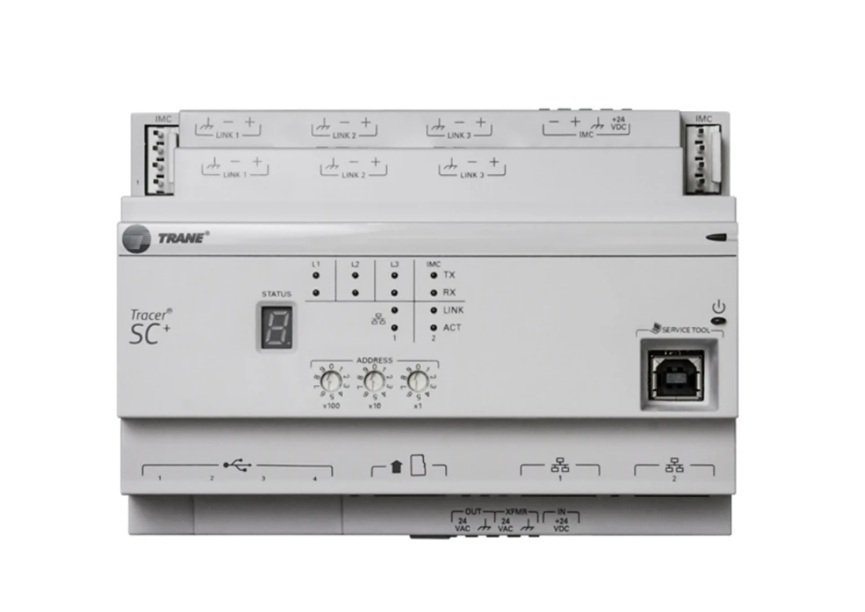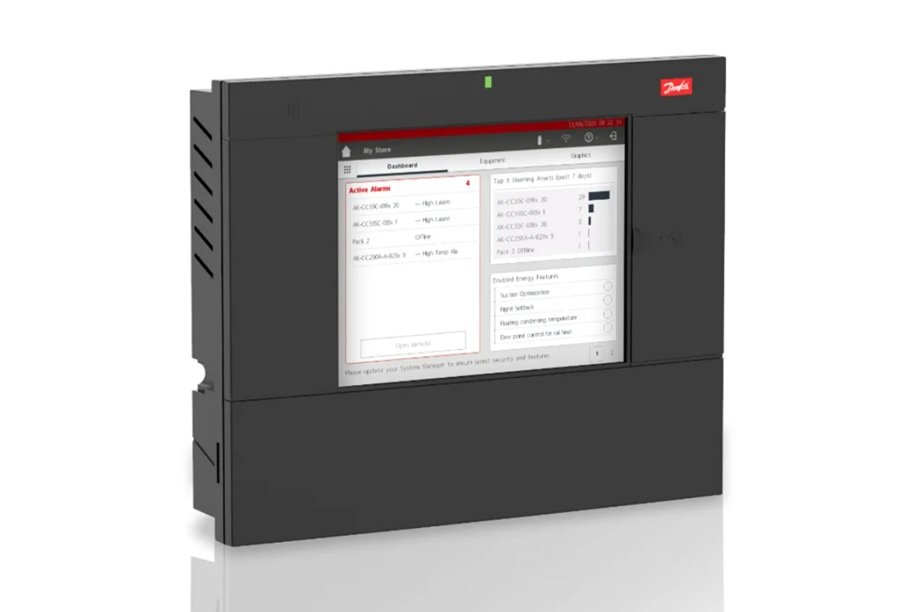
Danfoss, Copeland and Trane have released or recommended software updates addressing cybersecurity vulnerabilities in controllers used for refrigeration and HVAC management. The vulnerabilities, identified by Claroty Team82 in separate research projects, affect the Danfoss AK-SM 800A, Copeland XWEB Pro and Trane Tracer platforms and include authentication bypass, command injection, denial-of-service and information disclosure issues. Trane’s advisories list Tracer SC, Tracer SC+ and Tracer Concierge as affected, while the Team82 research was carried out on the Tracer SC+.
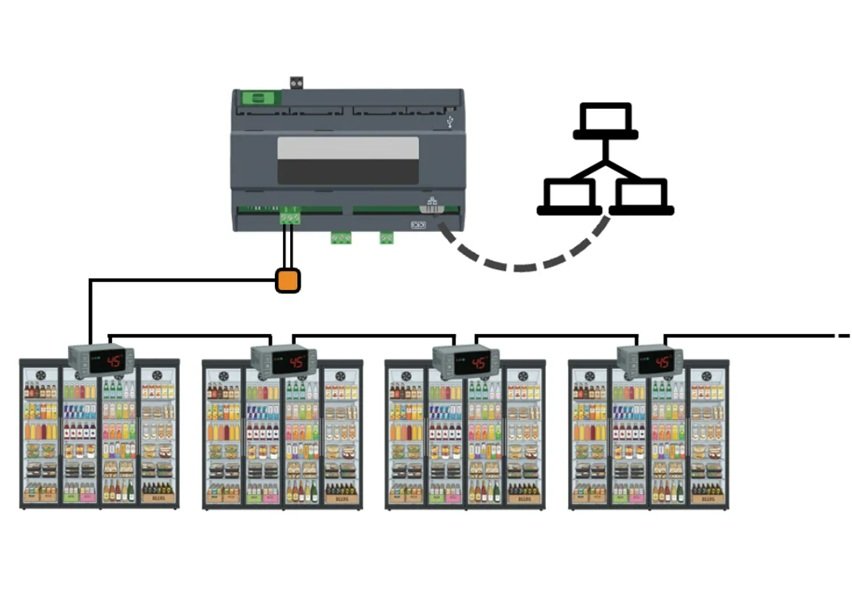
In the Danfoss AK-SM 800A, a centralized system manager used to coordinate refrigeration controllers, Team82 identified three vulnerabilities affecting the embedded web management interface. Researchers also examined the platform’s Internet exposure using Shodan and Censys and reported finding numerous publicly accessible management interfaces, with a Censys scan showing 2,765 internet-exposed devices. The scan reflects reachable management interfaces and does not indicate how many run vulnerable firmware.
CVE-2025-41450 concerns a hidden “code-of-the-day” authentication mechanism. Team82 found that the controller generates a daily authentication password based on its current date and reconstructed the algorithm used to produce the code. According to the researchers, reproducing the algorithm could allow an attacker to bypass the configured administrator password and obtain an authenticated administrative session.
A second Danfoss vulnerability, CVE-2025-41451, affects the SMTP email configuration. Team82 found that the email authentication password is formatted into an operating-system shell command without sanitization, creating a command-injection path that can lead to remote code execution. CVE-2025-41452 affects functionality that allows the web application to replace the headers.conf file used by the externally exposed Nginx instance. Researchers said an authenticated attacker could inject routing directives and trigger a crash of the sm_app process, resulting in denial-of-service of the management interface. Danfoss addressed the three vulnerabilities in firmware R4.3.1 and advises operators of affected AK-SM 800A controllers to upgrade to R4.3.1 or later.
Team82 separately identified 23 vulnerabilities in Copeland’s XWEB Pro supervisory controller platform, including the XWEB300D PRO and XWEB500D PRO. Of the 23 vulnerabilities, 21 were described by the researchers as high-severity. XWEB Pro controllers provide centralized management of refrigeration equipment and communicate with field controllers over an RS485 serial network, typically using Modbus.
CVE-2026-25085 is an authentication bypass affecting the XWEB Pro’s Lua-based middleware. When an unrecognized authentication mode is supplied, the authentication function can return an empty table that Lua evaluates as “truthy.” Because the routing logic checks for the existence of the returned object rather than its contents, Team82 found that an attacker could gain unauthenticated access to protected administrative API endpoints.
Another Copeland issue, CVE-2026-21718, involves deterministic administrator credentials generated using the current date, the device MAC address and hard-coded cryptographic keys stored in the firmware. Team82 said the algorithm can be reproduced to derive administrator credentials. Researchers also uncovered 19 OS command-injection vulnerabilities across API and CGI endpoints, where user-controlled data was passed into operating-system commands without proper sanitization. Successful exploitation can result in root-level code execution.
To demonstrate the physical consequences, Team82 connected an XR60CX field controller to an XWEB Pro controller over a serial Modbus connection. Researchers demonstrated manipulation of the temperature displayed by the XR60CX between -50°C and 110°C and control of refrigeration components. In another test, the cooling fans were disabled while the legitimate temperature measured by the probe continued to be displayed. Copeland patched the vulnerabilities in XWEB Pro firmware version 1.13.
The third investigation, published in June, covered Trane’s Tracer SC+ HVAC controller, a building management platform used in data centres and other facilities where a cooling failure can trigger thermal shutdowns and equipment damage. Team82 identified five vulnerabilities, including CVE-2026-28252 in the Trane Diagnostic Service, a remote-access feature intended for authorized Trane personnel. Researchers found that its challenge-response authentication algorithm is deterministic and can be calculated without knowing a secret, potentially providing root-level shell access. The SSH service is disabled by default, and this vulnerability is exploitable only if the service has been manually enabled.
CVE-2026-28253 is a pre-authentication denial-of-service vulnerability in the Trane server handling HTTP and BACnet connections. Team82 found that the server does not limit HTTP header size and can continue allocating memory when receiving data without newline characters until allocation fails. CVE-2026-28254 covers API routes accessible without authentication that expose information including device details, connected devices, BACnet reports and cached GUI assets.
Team82 also identified CVE-2026-28255, involving encrypted hardcoded credentials used for Trane remote services and shared across all devices globally, and CVE-2026-28256, covering hardcoded security-relevant constants. The latter include encryption keys used for configuration data as well as keys associated with backups and firmware updates. Trane recommends updating Tracer SC+ controllers to version v6.3, released March 1, 2026, or later. The vendor’s CVE advisories identify the release as v6.30.2313.
Claroty Team82 disclosed the findings to the respective manufacturers as part of coordinated disclosure processes, and all three issued fixes: Danfoss firmware R4.3.1 for the AK-SM 800A, Copeland firmware 1.13 for XWEB Pro, and Trane version v6.3 or later for Tracer SC+.
Beyond patching, both Danfoss and Trane advise against exposing controller management interfaces directly to the Internet. Danfoss recommends restricting administrative access to trusted management networks or securing it through VPNs and network segmentation, and Trane states that its systems should be isolated from the public Internet. For sites running affected controllers, the practical steps are to confirm the installed firmware version, apply the vendor update, remove any direct Internet exposure of the web management interface, and check whether optional remote-access services such as SSH have been enabled during commissioning or service work.